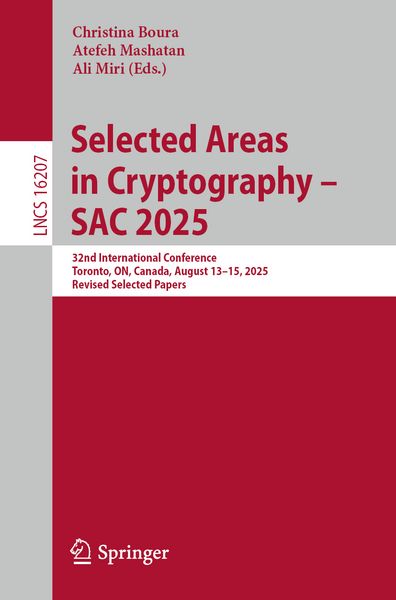
Selected Areas in Cryptography – SAC 2025 32nd International Conference, Toronto, ON, Canada, August 13–15, 2025, Revised Selected Papers
-
- Taschenbuch ausgewählt
- eBook
-
Sprache:Englisch
79,99 €
inkl. gesetzl. MwSt.,
Beschreibung
Produktdetails
Einband
Taschenbuch
Erscheinungsdatum
03.01.2026
Abbildungen
XXI, 806 p. 131 illus., 98 illus. in color.
Herausgeber
Christina Boura + weitereVerlag
SpringerSeitenzahl
806
Maße (L/B/H)
23,5/15,5/4,5 cm
Gewicht
1229 g
Sprache
Englisch
ISBN
978-3-032-10535-6
This book contains revised selected papers from the 32nd International Conference on Selected Areas in Cryptography, SAC 2025, held in Toronto, ON, Canada, in August 2025.
The 29 full papers were presented in this volume were carefully reviewed and selected from 109 submissions. They were organized in the following topical sections as follows : Cryptanalysis of Symmetric Schemes and Primitives; Impossible Differential Attacks; Symmetric Design Strategies and Security; Efficient Implementations; Public Key Encryption; Attacks on Public-Key Schemes; Isogeny-Based Cryptography; Fully Homomorphic Encryption; and Side-Channel Analysis and Fault Attacks.
Noch keine Bewertungen vorhanden
Verfassen Sie die erste Bewertung zu diesem Artikel
Helfen Sie anderen Kundinnen und Kunden durch Ihre Meinung.
Kurze Frage zu unserer Seite
Vielen Dank für dein Feedback
Wir nutzen dein Feedback, um unsere Produktseiten zu verbessern. Bitte habe Verständnis, dass wir dir keine Rückmeldung geben können. Falls du Kontakt mit uns aufnehmen möchtest, kannst du dich aber gerne an unseren Kund*innenservice wenden.
zum Kundenservice