Managing Risk and Information Security Protect to Enable
-
- Englisch ausgewählt
-
Auflage:2nd ed.
- 1st ed. 37,99 €
- 2nd ed. 28,99 € ausgewählt
28,99 €
inkl. gesetzl. MwSt.,
Beschreibung
Produktdetails
Einband
Taschenbuch
Erscheinungsdatum
11.08.2016
Abbildungen
XXVII, 187 p. 20 illus. in color.
Verlag
ApressSeitenzahl
187
Maße (L/B/H)
23,5/15,5/1,2 cm
Gewicht
335 g
Auflage
2nd ed.
Sprache
Englisch
ISBN
978-1-4842-1456-5
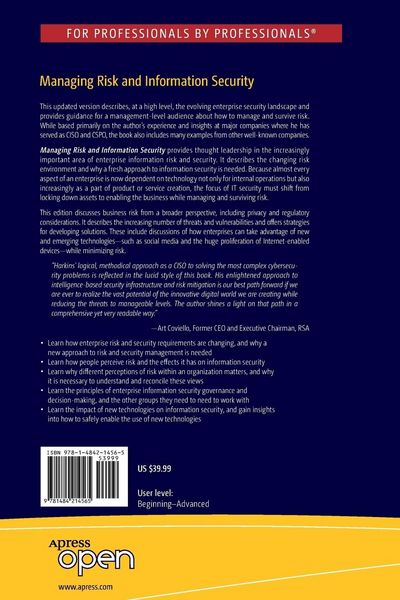
Examine the evolving enterprise security landscape and discover how to manage and survive risk. While based primarily on the author’s experience and insights at major companies where he has served as CISO and CSPO, the book also includes many examples from other well-known companies and provides guidance for a management-level audience.
Managing Risk and Information Security
provides thought leadership in the increasingly important area of enterprise information risk and security. It describes the changing risk environment and why a fresh approach to information security is needed. Because almost every aspect of an enterprise is now dependent on technology not only for internal operations but increasing as a part of product or service creation, the focus of IT security must shift from locking down assets to enabling the business while managing and surviving risk.
This edition discusses business risk from a broader perspective, including privacy and regulatory considerations. It describes the increasing number of threats and vulnerabilities and offers strategies for developing solutions. These include discussions of how enterprises can take advantage of new and emerging technologies—such as social media and the huge proliferation of Internet-enabled devices—while minimizing risk.
What You'll Learn
Review how people perceive risk and the effects it has on information security
- See why different perceptions of risk within an organization matters
- Understand and reconcile these differing risk views
Gain insights into how to safely enable the use of new technologies
Who This Book Is For
The primary audience is CIOs and other IT leaders, CISOs and other information security leaders, IT auditors, and other leaders of corporate governance and risk functions. The secondary audience is CEOs, board members, privacy professionals, and less senior-level information security and risk professionals.
"Harkins’ logical, methodical approach as a CISO to solving the most complex cybersecurity problems is reflected in the lucid style of this book. His enlightened approach to intelligence-based security infrastructure and risk mitigation is our best path forward if we are ever to realize the vast potential of the innovative digital world we are creating while reducing the threats to manageable levels. The author shines a light on that path in a comprehensive yet very readable way."
—Art Coviello, Former CEO and Executive Chairman, RSA
Noch keine Bewertungen vorhanden
Verfassen Sie die erste Bewertung zu diesem Artikel
Helfen Sie anderen Kundinnen und Kunden durch Ihre Meinung.
Kurze Frage zu unserer Seite
Vielen Dank für dein Feedback
Wir nutzen dein Feedback, um unsere Produktseiten zu verbessern. Bitte habe Verständnis, dass wir dir keine Rückmeldung geben können. Falls du Kontakt mit uns aufnehmen möchtest, kannst du dich aber gerne an unseren Kund*innenservice wenden.
zum Kundenservice