KI-Beratung Beta

Gutscheinbedingungen

**Gültig vom 05.10.2026 bis 07.10.2026 | Gültig für nicht preisgebundene fremdsprachige Bücher | Einzelne Artikel können ausgeschlossen sein | Online auf www.bücher.de einlösbar | Click & Collect nur mit Online-Zahlung (Paypal/Kreditkarte) vorab | Nicht kombinierbar mit anderen Gutscheinen oder Preisaktionen | Nur einmal pro Einkauf einlösbar | Gutschein wird auf max. 500€ Bestellwert angerechnet | Keine Barauszahlung | Nicht gültig für Versandkosten und Services

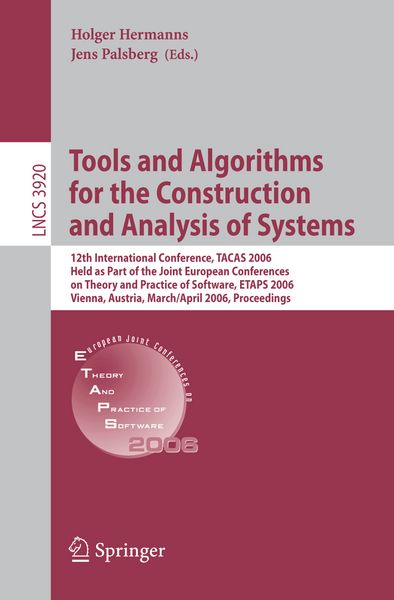
Produktbild: Tools and Algorithms for the Construction and Analysis of Systems
Band 3920

Tools and Algorithms for the Construction and Analysis of Systems 12th International Conference, TACAS 2006, Held as Part of the Joint European Conferences on Theory and Practice of Software, ETAPS 2006, Vienna, Austria, March 25 - April 2, 2006, Proceedings

49,99 €

inkl. gesetzl. MwSt., Versandkostenfrei


Beschreibung

Produktdetails

Einband

Taschenbuch

Erscheinungsdatum

15.03.2006

Abbildungen

XVI, 512 p.

Herausgeber

Holger Hermanns + weitere

Verlag

Springer Berlin

Seitenzahl

512

Maße (B/H)

15,2/22,9 cm

Gewicht

762 g

Sprache

Englisch

ISBN

978-3-540-33056-1

Beschreibung

Produktdetails

Einband

Taschenbuch

Erscheinungsdatum

15.03.2006

Abbildungen

XVI, 512 p.

Herausgeber

Verlag

Springer Berlin

Seitenzahl

512

Maße (B/H)

15,2/22,9 cm

Gewicht

762 g

Sprache

Englisch

ISBN

978-3-540-33056-1

Herstelleradresse

Springer-Verlag GmbH
Heidelberger Platz 3
14197 Berlin
Deutschland
Email: sdc-bookservice@springer.com
Url: www.springer.com
Telephone: +49 30 827870
Fax: +49 30 8214091

Noch keine Bewertungen vorhanden

Verfassen Sie die erste Bewertung zu diesem Artikel

Helfen Sie anderen Kundinnen und Kunden durch Ihre Meinung.

Kundinnen und Kunden meinen

Bewertungen (0)

  • Produktbild: Tools and Algorithms for the Construction and Analysis of Systems
  • Invited Contributions.- Weighted Pushdown Systems and Trust-Management Systems.- Parametrization and Slicing.- Automatic Verification of Parameterized Data Structures.- Parameterized Verification of ?-Calculus Systems.- Easy Parameterized Verification of Biphase Mark and 8N1 Protocols.- Evaluating the Effectiveness of Slicing for Model Reduction of Concurrent Object-Oriented Programs.- Symbolic Techniques.- New Metrics for Static Variable Ordering in Decision Diagrams.- Widening ROBDDs with Prime Implicants.- Efficient Guided Symbolic Reachability Using Reachability Expressions.- Satisfiability.- SDSAT: Tight Integration of Small Domain Encoding and Lazy Approaches in a Separation Logic Solver.- SAT-Based Software Certification.- Expressiveness + Automation + Soundness: Towards Combining SMT Solvers and Interactive Proof Assistants.- Exploration of the Capabilities of Constraint Programming for Software Verification.- Abstraction.- Counterexample-Guided Abstraction Refinement for the Analysis of Graph Transformation Systems.- Why Waste a Perfectly Good Abstraction?.- Efficient Abstraction Refinement in Interpolation-Based Unbounded Model Checking.- Approximating Predicate Images for Bit-Vector Logic.- Model Checking Algorithms.- Finitary Winning in ?-Regular Games.- Efficient Model Checking for LTL with Partial Order Snapshots.- A Local Shape Analysis Based on Separation Logic.- Program Verification.- Compositional Model Extraction for Higher-Order Concurrent Programs.- A Region Graph Based Approach to Termination Proofs.- Verifying Concurrent Message-Passing C Programs with Recursive Calls.- Automata-Based Verification of Programs with Tree Updates.- Runtime Diagnostics.- An Experimental Comparison of the Effectiveness of Control Flow Based Testing Approaches onSeeded Faults.- Exploiting Traces in Program Analysis.- Quantitative Techniques.- Model-Checking Markov Chains in the Presence of Uncertainties.- Safety Metric Temporal Logic Is Fully Decidable.- Simulation-Based Graph Similarity.- Tool Demonstrations.- PRISM: A Tool for Automatic Verification of Probabilistic Systems.- DISTRIBUTOR and BCG_MERGE: Tools for Distributed Explicit State Space Generation.- mcmas: A Model Checker for Multi-agent Systems.- MSCan – A Tool for Analyzing MSC Specifications.- Refinement.- A Practical and Complete Approach to Predicate Refinement.- Counterexample Driven Refinement for Abstract Interpretation.- Abstraction Refinement with Craig Interpolation and Symbolic Pushdown Systems.